Wednesday, June 18, 2008

The application of third party certification programme in Malaysia


Third-parties called certificate authority issues digital certificates used to create digital signatures and public-private key pairs. The role of the third party in this process is to guarantee that the individual granted the unique certificate is, in fact, who he or she claims to be certificate authority are a critical component in data security and e-commerce because they guarantee that the two parties exchanging information are really who they claim to be. A digital certificate is an electronic certificate that establishes your credentials when doing business or other transactions on the Web. The certificate is issued by a Certification Authority (CA).

Example of third party in Malaysia is MSC Trustgate.com Sdn Bhd(www.msctrustgate.com). It is a licensed Certification Authority (CA) operating out of the Multimedia Super Corridor. MSC Trustgate was incorporated in 1999 to meet the growing need for secure open network communications and become the catalyst for the growth of e-commerce, both locally and across the ASEAN region. In present, MSC Trustgate has 12 million in paid up capital.

Trustgate has been licensed under the Digital Signature Act 1997 (DSA), a Malaysia law that sets a global precedent for the mandate of a CA. As a CA, Trustgate’s core business is to provide digital certification services, including digital certificates, cryptographic products, and software development.

Verisign is the leading Secure Sockets Layer (SSL) Certificate Authority enabling secure e-commerce, communications, and interactions for Web sites, intranets, and extranets. Choose the most trusted mark on the Internet and enable the strongest SSL encryption available to every site visitor.

The application of third parties certificate in Malaysia are when a website visitor connects to a web server using digital certificate they will see that the URL in the address bar begins with https:// rather than the usual http:// and also a small gold padlock will appear in their browser, e.g.
As seen by users of Internet Explorer
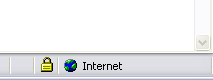


Whenever a browser connects to a webserver (website) over https:// - this signifies that the communication will be encrypted and secure. The actual complexities of the digital certificate protocol remain invisible to the end customer.

All digital certificates are issued to either companies or legally accountable individuals. Typically SSL Certificates contain the domain name, the company name, the address i.e. city, state and country. It will also contain the expiry date of the Certificate and details of the Certification Authority responsible for the issuance of the Certificate.

When a browser connects to a secure site it will retrieve the site's digital certificate and check that it has not expired, that it has been issued by a Certification Authority the browser trusts and that it is being used by the website for which it has been issued. If it fails on any one of these checks the browser will display a warning to the end user.


So both party in a deal are protected. The buyer mail the payment to the escrow services , which verify the payment and alert the seller when every things check out. At that point, the seller ship the goods to the buyer . after an agreed upon inspection period, the buyer notifies the service, which then send a escrow services. So. it impletation help to improve customers trust between both seller and buyer

As a conclusion, the application of third party certification programme in Malaysia make the online dealing more safety and increase trustiness
.

The treat of online security: How safe is our data?


Nowadays, getting more people using the internet to communicate with others, search for information and also engaged in the online transaction. Internet give us become more convenient because internet is an easy and useful tool that help people to do thing with lesser cost and more efficiency.But, as the internet users display more of their personal information on social networking web sites, and office workers upload more sensitive data to online software programs, computer hackers are employing increasingly sophisticated methods to pry that information loose. In many cases, they are devising small attacks that can go into traditional security software, while exploiting the trust users place in popular business and consumer Web sites.
Threats to e-commerce systems can be either malicious or accidental. Malicious threats could include hackers attempting to penetrate a system to read or alter sensitive data, burglars stealing a server or laptop that has unprotected sensitive data on its disk, imposters posing as legitimate users and even creating a website similar to yours, authorized users downloading a web page or receiving an email with hidden active content that attacks your systems or sends
sensitive information to unauthorized people.

Some of the more common threats that hackers pose to e-commerce systems include carrying out denial-of-service (DoS), attacks that stop access to authorized users of a website, so that the site is forced to offer a reduced level of service or, in some cases, ceases operation completely, gaining access to sensitive data such as price lists, catalogues and valuable intellectual property, and altering, destroying or copying it altering the company’s website, thereby damaging company’s image or directing the customers to another site, gaining access to financial information about the business or customers, with a view to perpetrating fraud and using viruses to corrupt business data. These kinds of targeted attacks on Web-based services may constitute the
top computer security threats of 2008 (BusinessWeek.com, 11/12/07).

As a conclusion, there are many threats to online security, so when doing online transaction must have proper safeguard such as encryption, digital certificate and firewall. With the safeguard, our data will be safer since the threat is so serious.

How to safeguard our personal and financial data?

Internet and all the on-line transaction have created convenient to all the users. However, there are getting more and more doubt on the internet security. There is a problem exist when user making transaction such as on-line banking. User will concern about the web security when they entering their private and confidential data into the system or website. It is especially important to take extra security precautions to safeguard the data in order to prevent lost of private and confidential information.
Encryption
(http://bluefive.pair.com/articles_encryption_and_decryption.htm )
How to safeguard our personal and financial data??? Encryption is one of the safeguard. Encryption is the conversion of data into a secret code for storage in the databases and transmission over network. The sender uses an encryption algorithm to convert the original message into a coded equivalent. At the receiving end the cipher text is decoded back into clear text. This can prevent leaking and lost of data.
Firewall
(http://www.articlesnatch.com/Article/Use-Network-Firewalls-To-Protect-Your-System/60788)
Besides, firewall can also protect user’s personal and financial data. Firewall is a system used to protect an organization’s intranet from the internet. It can be used to verify an outside user of the network, verify his or her level of access authority, and then direct the user to the program, data, or service requested. Most organization is using firewall to
protect their private and confidential information.
Password
(http://www.securityfocus.com/infocus/1192 )
Other than that, creating secure passwords is also very important to safeguard our personal and financial data. Password is a secret code entered by the user to gain access to systems, applications data, or a network server. If the user cannot provide the correct password, the operating system should deny access. This can limited to those user that has password can access to the system.

As a conclusion, there is also other method to safeguard our personal and financial data. Adequate and appropriate safeguard is very important to each and every user as well as the organization in order to maintain correct and clear data or information.


Wednesday, June 11, 2008

How e-commerce can reduce cycle time, improve employees’ empowerment and facilitate customer support?

Why use E-commerce??
Reduce Cycle Time
Traditionally, producers sell their products to customers through intermediaries such as wholesaler and retailer. E-commerce eliminates those middlemen between sellers and buyers by removing links from trading chain and put producers directly in touch with the customers. It provides a 24 hours store that also reduces sale cycle and reduces unnecessary phone calls and mailings.

Improves Employees’ Empowerment
E-commerce also improves employees’ empowerment where provides enabling technologies for the company’s employees. It can improve employee knowledge and effectiveness, which reduces contact handle times. Other than that, E-commerce increase employees’ empowerment by providing better decision support and reference tools and provide desktop enhancement for employees for data access and retrieval. Thus, it improves employees’ morale and loyalty.

Facilitates Customer Support
On the consumer level, an individual can go online to purchase anything from books, grocery to expensive items like real estate, online bill payments, buying stocks, transferring funds from one account to another, and initiating wire payment to another country. All these activities can be done with a few keystrokes on the keyboard. Using e-commerce gives customers the opportunity and shop at their convenience and at their place. They can access into e-commerce from home, office, or on the road, 24 hours a day, and 7 days a week. Besides, it slowly builds loyalty since it is so convenient and saves time.

The history and evolution of E-Commerce

The word E-Commerce or electronic commerce was founded late in the 1970’s. The term was introduced for transactions done via computer to computer.

There have been several key steps in the history and evolution of E-Commerce. To interchange data and to carry out business deals electronically in 1960’s Electronic Data Interchange (EDI) was formulated. Initially ecommerce was facilitating business transactions electronically using technology such as EDI (electronic data interchange) and EFT (electronic funds transfer) to send business documents such as purchase orders or invoices. However, in 1984 the ASC X12 standard became stable and reliable in transferring large amounts of transactions. In 1969 ARPANET, was developed by Americas department of defence for researching new reliable networks and later this enhanced into Internet that was purely used as a research tool for nearly 20yrs.

In 1991, Tim Berners-Lee developed World Wide Web at CERN that started the first Internet transaction. These technology supported exchange of data that was in text format only. The next major step occurred in 1993, Mosiac was developed by Marc Andreessen, this is the first graphic web browser. The Mosaic browser was quickly adapted into a downloadable browser. Netscape, the most successful graphic browser was later developed by Marc Andreessen. On the other hand, Microsoft came up with Microsoft Internet Explorer. The first business deal took place in 1994 and since then there have been billions of dealings.

Later in 1998 DSL was launched into the market that provided much faster access and persistent connection to the internet. A major merger, in early 2000, between AOL and Time Warner was another major push for electronic commerce. The merger, worth $350 million, brought together a major online company with a traditional company. In February 2000 hackers attacked some major players of E-Commerce, including Yahoo, eBay and Amazon. In light of these attacks the need for improved security in the development of electronic commerce

As the websites grew the importance of internet today is thousands of times what it was only a decade ago. E-Commerce is a new form of business that has developed rapidly. It provides a different mode of doing business that helps reduce labour cost and much faster transaction

An example of E-commerce success and it causes


E-commerce is defined as “the sharing of business information, maintaining business relationships and conducting business transactions by means of telecommunications networks”. It also includes various processes within and outside the organization in addition to buying and selling activities.

Generally, there are some rules for a successful e-commerce website. First of all, the retailer has a product or products that meet the customer need. After that, the retailer needs to use the website to advertise the product and make the website as attractive as possible, displays the product to best advantage.

For online payment systems and credit card processing, the retailer must ensure that customers feel secure in the online transaction. It is because customers are very concern about the level of security when providing sensitive information online and will use e-commerce only when they develop a certain level of trust. So the retailer must ensure the transaction is fully secured and no unauthorized access. The retailer makes it easy for customers to purchase products
by using the credit card or e-banking systems.

The success case of e-commerce is bookseller
www.ABE.com , with no venture capital, is presently
slaughtering the VC-funded S.F. ABE.com did a lot of things right on the web, they put up a simple, user-friendly web site that delivered what the customers wanted, a good selection of used books at good prices.

But they did even more things right at the back end. For example, they left the books right where they were, sitting in low-rent used bookstore space. Alibris took possession of the books, piling up warehouse rental costs, labor costs, and doubling their shipping costs. ABE.com acted modestly, an appropriate stance in the quiet world of used bookselling. Alibris spend money with splashy advertisements in New Yorker magazine. ABE.com went out of their way to accommodate computer-illiterate used booksellers, by accepting inventory data in virtually any format. And not least, ABE.com answered the telephone, and they were pleasant to customers and suppliers alike.

As a conclusion, E-commerce success is not so easy, it need a clear vision and goal, patient and long-term view and embrace technology and change.

An example (pets.com) of an E-commerce failure and its cause


Today, businessmen are expending their business through internet in order to compete with their competitor. Businesses often rely on the Web to attract clients, communicate with suppliers, and generate revenues. As a result, the cost of failed online transactions can be significant even a single hour of downtime could cost a retailer thousands of dollars in lost sales. The use of the internet and web to transact business is called E-commerce. E-commerce had brought success to most of the businessman. However, there are also some failures. Now, let us look at some causes of failure in E-commerce and a real world example.


Causes of failures in E-commerce
The causes of failures in E-commerce can divide into four categories namely: software failures, operator error, hardware failures, and security violations. Software failure is failures occur during routine maintenance, software upgrades and system integration. Operator error occurs when the operator either omits an action or executes an incorrect action during system maintenance. Other than that, a hardware failure is also one of causes of E-commerce failure. It can occur for several reasons, for example, wear and tear of mechanical parts and loose wiring. Besides, some common security violations that occur in websites are password disclosures, Denial of Service (DOS) attacks, worms and viruses and theft.


A real life example
Pets.com (1998-2000) The important dot-com lesson was that advertising, never able to give pet owners a persuasive reason to buy pet online. Afteno matter how clever, cannot save you. Pets.com was r they ordered a pet, a customer had to wait a few days to actually get it. Moreover, because the company had to undercharge for shipping costs to attract customers, it actually lost money on most of the items it sold.

As a conclusion, all of the relailer need to enhance their operation and maintenance in order to prevent failure and become success in E-commerce.